AI Security Risks: Prompt Injection, Deepfakes, and How to Protect Your Business
The rapid enterprise rollout of Generative AI, Large Language Models (LLMs), and autonomous agents has unlocked transformative operational efficiencies—while simultaneously introducing an entirely new class of critical threat vectors. Traditional firewalls and web application filters are blind to cognitive-layer exploits. From direct and indirect prompt injection attacks that hijack internal AI copilots to hyper-realistic synthetic voice and video deepfakes weaponized for high-stakes financial fraud, businesses are facing an unprecedented attack surface that conventional cybersecurity programs were never designed to defend against.
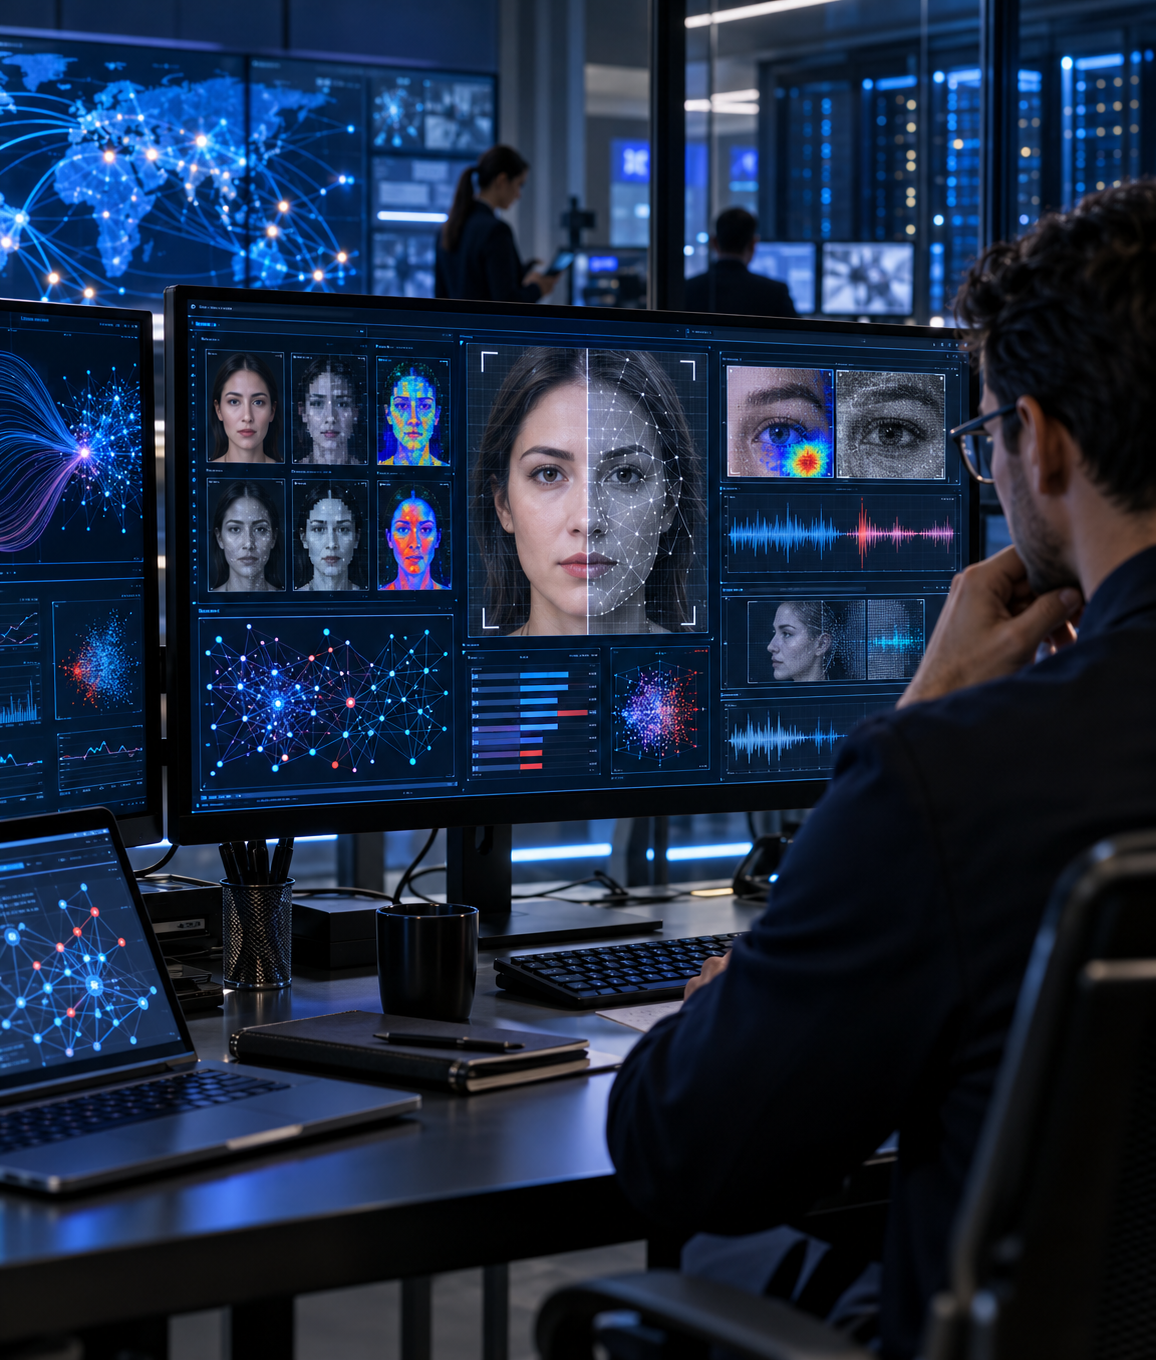
Protecting your enterprise begins with addressing the top vulnerability categories defined by the OWASP Top 10 for LLMs. Direct prompt injections override system instructions to exfiltrate proprietary source code or confidential training data, while indirect prompt injections hide adversarial payloads inside ingested emails, PDFs, or web feeds to manipulate Retrieval-Augmented Generation (RAG) pipelines. Concurrently, generative deepfake technologies have transformed executive impersonation (vishing and synthetic video conference deception), leading to multi-million-dollar unauthorized wire transfers. Mitigating these threats demands multi-tiered defenses: implementing real-time AI firewalls and input/output guardrails, enforcing out-of-band biometric verification protocols for sensitive transactions, and enforcing strict least-privilege API scoping on all internal autonomous agents.
"Generative AI hasn't just enhanced enterprise productivity—it has fundamentally automated the adversary's playbook. If your security architecture treats LLM outputs as trusted or relies solely on voice and video recognition to authenticate financial authorization, your organization is already vulnerable."
Principal AI Security Researcher, Cyber Skill Nexus
At Cyber Skill Nexus, we assist organizations in safely adopting and scaling AI technologies. Our offensive security teams conduct rigorous LLM Red Teaming and prompt injection stress testing across your custom models, APIs, and copilot workflows. In parallel, our defensive consultants deliver tailored executive anti-deepfake verification protocols, zero-trust data governance strategies, and automated guardrails to ensure your business leverages AI innovation without compromising enterprise security.